
What Is ISO 27001 Certification?
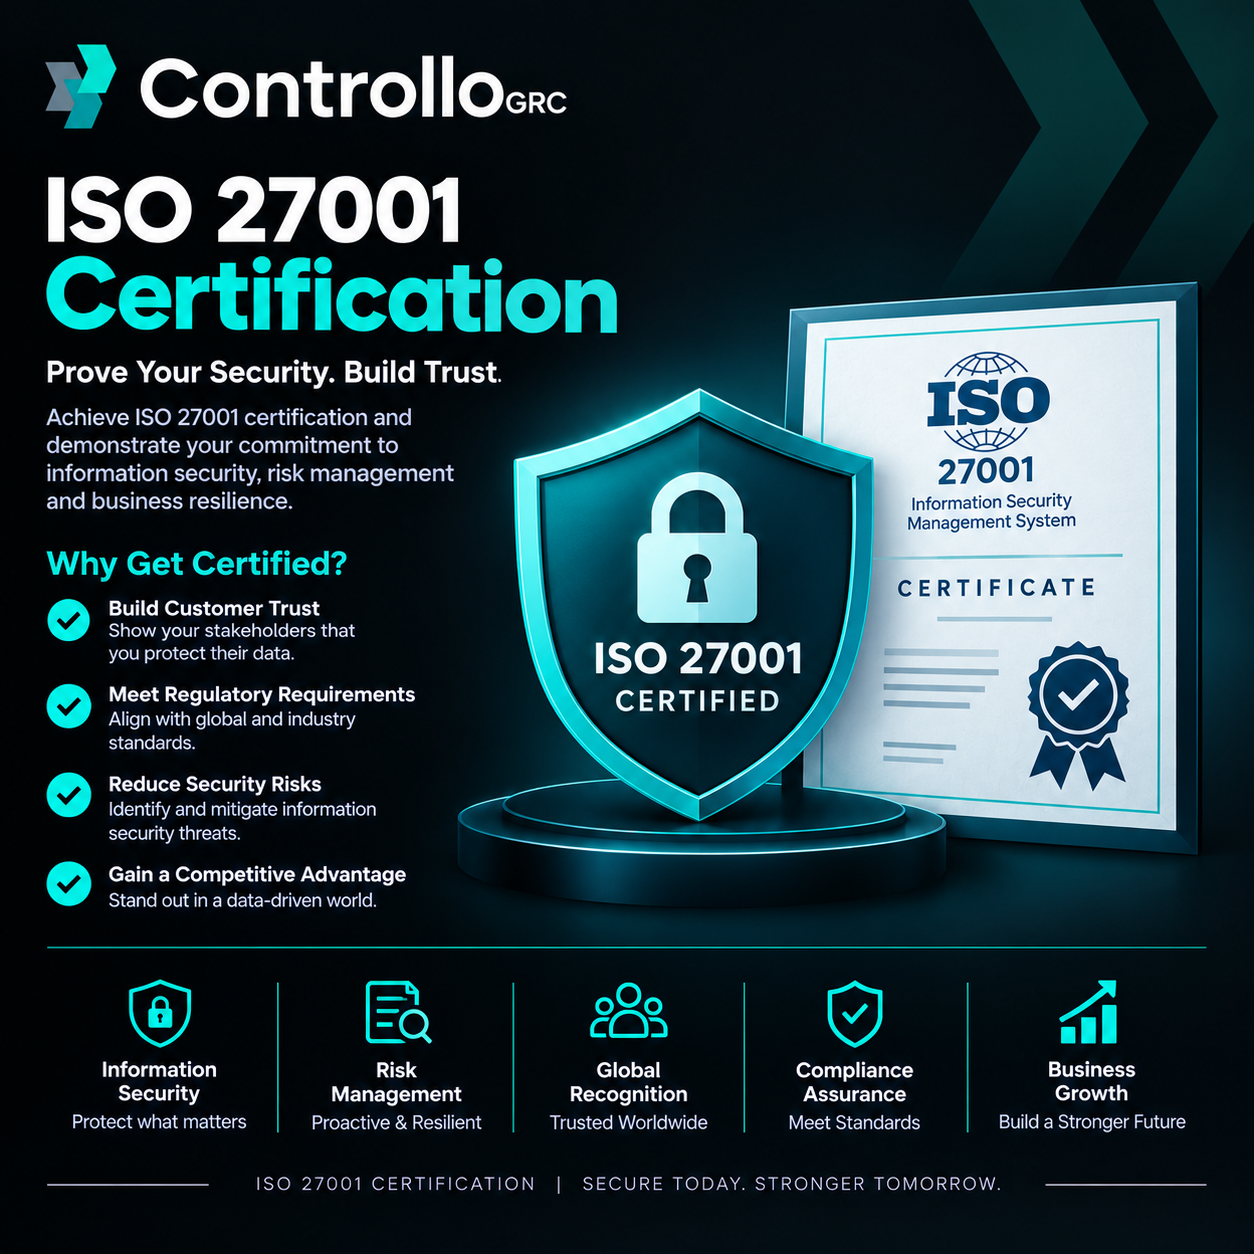
ISO 27001 Certification ISO/IEC 27001 is the global benchmark standard that demonstrates an organization's ISMS complies with the applicable standards of ISO/IEC 27001. This includes how an organization manages information security risks, design and implement safeguards, allocate responsibilities, measure success and drive continual improvement.
What Does the Certification Cover?
The scope of ISO 27001 Certification is related to the whole of the Information Security Management System (ISMS) of the organization: how it manages security risks, applies safeguards, maintains performance, and achieves continuous improvement. For US organizations, this quality assurance helps build a baseline for systematic information security safeguards for customer data, proprietary business information, and mission-critical systems. Controllo.ai is an ISO 27001-level readiness tool that takes care of everything.
- Risk assessment and treatment: Identify information security risks and determine how to address them.
- Security controls: Apply appropriate organizational, people, physical, and technological controls.
- Policies and documentation: Maintain security policies, procedures, risk assessments, and supporting records.
- Access and asset management: Manage access permissions, information assets, and responsibilities.
- Incident management: Establish processes to report, respond to, and learn from security incidents.
- Internal audits and reviews: Evaluate ISMS effectiveness and address identified gaps.
- Continual improvement: Monitor performance and improve the management system over time.
Who Issues the Certificate?
ISO 27001 Certification is given by an independent certification body once it audits an ISMS of an organisation and verifies that an organisation is fulfilling the relevant ISO/IEC 27001 requirements. The ISO creates and publishes the standard but it does not perform certifications for individual organisations. US companies can increase trust in a certification by selecting a certification body that is accredited by a recognised accreditation body.
Who Needs ISO 27001 Certification?
ISO 27001 Certification can be advantageous to your organisation if you require auditable assurance of how you manage information security for your clients, partners, regulators or procurement team. Certification to the standard isn't a legal requirement, of course, but it can satisfy clients, enhance vendor audits and provide reassurance of information security controls.


