
What Does an ISO 27001 Consultant Do?
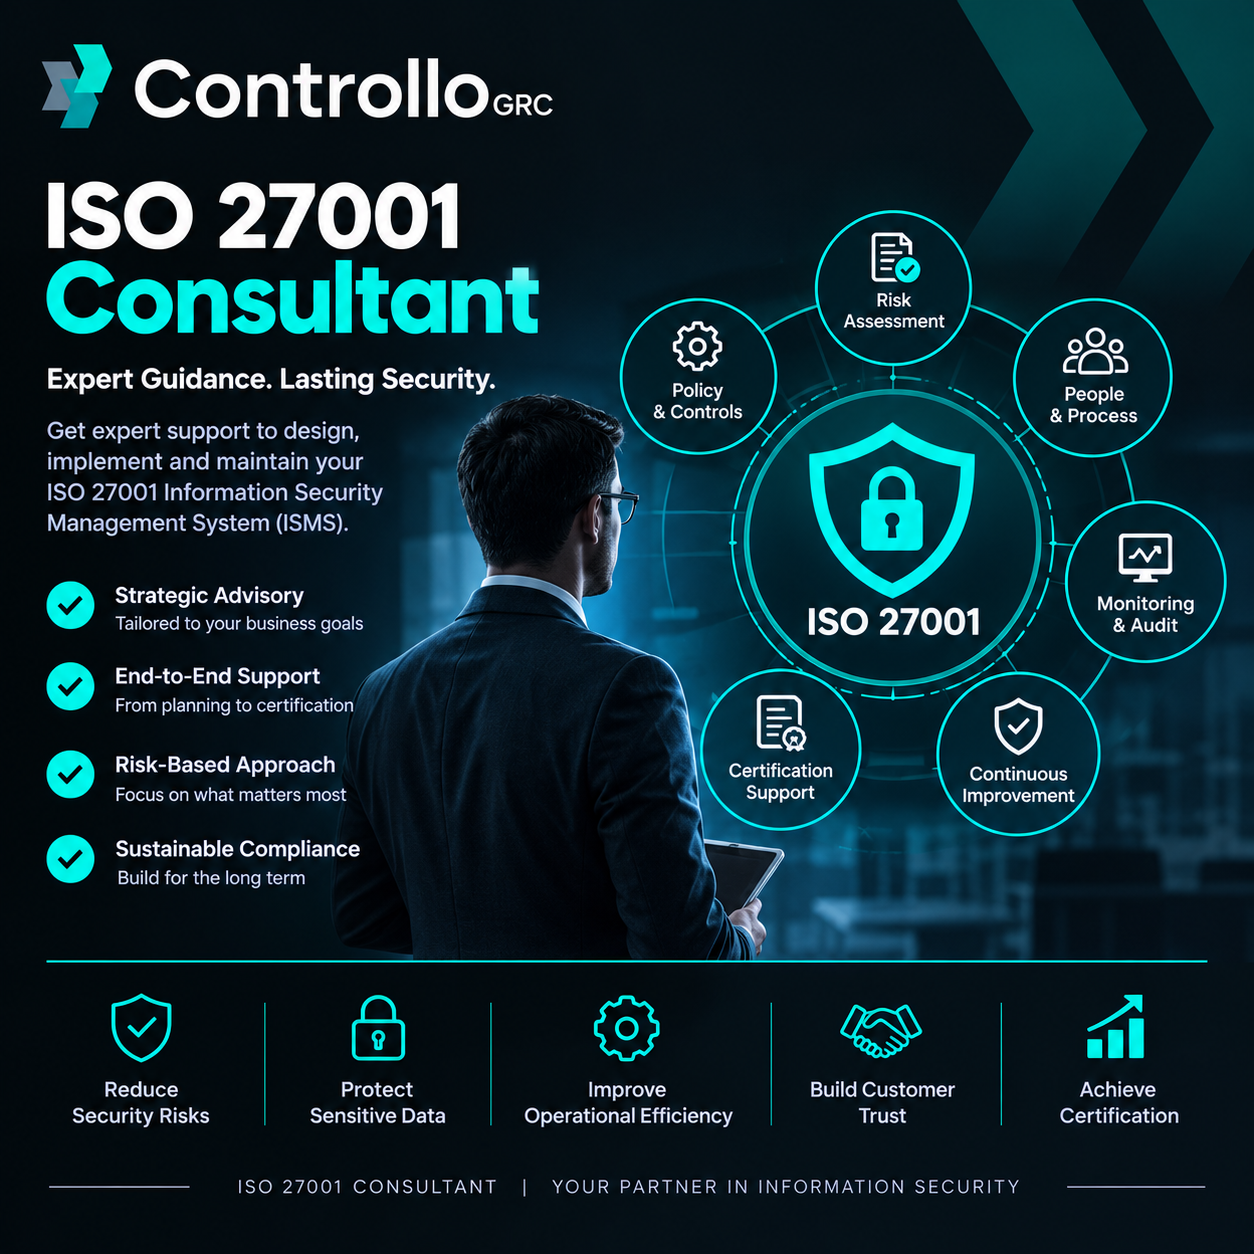
An ISO 27001 Consultant defines an Information Security Management System (ISMS) and plans the implementation of an Information Security Management System; to accomplish that, she will be responsible for assessing security gaps, determining the risk level, recommending controls, and creating documentation material for audit day. Additionally, the consultant has to support organizations with risk assessment, writing security policies, security awareness, design and execution of internal audits, and preparation for audits. ISO 27001 compliance, in today's technology-driven world, is key to timely achievement of certification and for that, technology-enabled ISO 27001 compliance support companies like Controllo.ai are the right choice.
Key responsibilities
- Gap analysis: Compare existing security practices with ISO/IEC 27001 requirements.
- Risk assessment: Identify threats to information and determine suitable risk treatments.
- ISMS documentation: Help develop policies, procedures, risk records, and a Statement of Applicability.
- Control implementation: Guide teams in selecting and applying relevant security controls.
- Audit preparation: Organize evidence, review processes, and address gaps before an independent certification audit.
- Ongoing improvement: Help establish monitoring, internal audit, corrective action, and management review processes.
Consultant vs. certification body
| Comparison Factor | ISO 27001 Consultant | ISO 27001 Certification Body |
|---|---|---|
| Primary Role | Guides organizations through ISO 27001 implementation | Independently evaluates compliance with ISO 27001 |
| Risk Assessment | Helps identify security risks and gaps | Reviews whether risks are appropriately addressed |
| ISMS Development | Supports ISMS policies, processes, and documentation | Audits the implemented ISMS |
| Control Implementation | Advises on selecting and implementing security controls | Assesses relevant controls during the audit |
| Audit Preparation | Helps prepare evidence and conduct readiness reviews | Performs the independent certification audit |
| Certification Decision | Cannot independently grant ISO 27001 certification in the role of consultant | Determines whether certification requirements are met |
| Controllo.ai Support | Helps organize compliance workflows and control-related activities | Can help organize evidence for audit preparation but does not replace the auditor |


